- Gov & Defense
Case Study: Secure Watchlist Distribution for Border Control
Law Enforcement Agency in the Middle East (GCC)
Extremely high exposure risk due to Internet-facing destination systems
Full database replication of a MS SQL Server Enterprise environment
Requirement for continuous availability and consistency of watchlist data
Need for secure high-availability architecture
Need / Problem / Context
Securing Real-Time Watchlist Access at Airport Borders
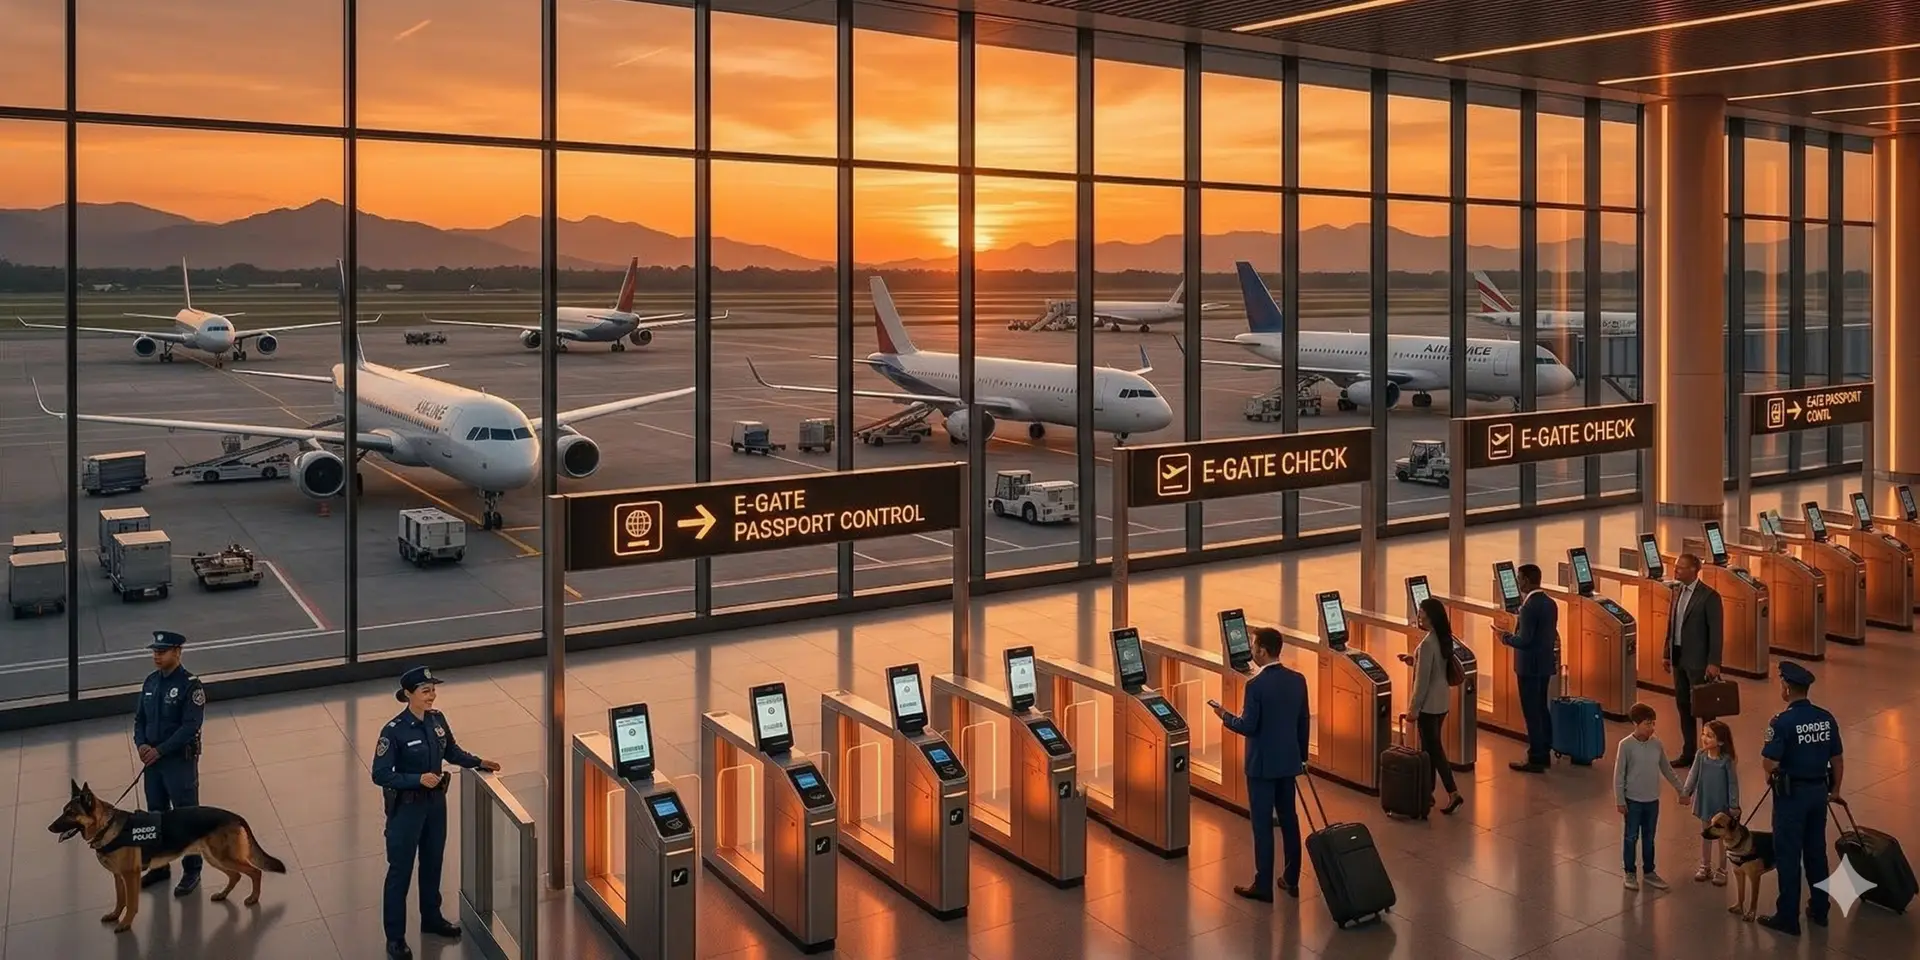
A government law enforcement agency needed to securely distribute a sensitive national watchlist database to an external application used at airport border control checkpoints. This application, partially exposed to the Internet, required continuous access to up-to-date data to support real-time identity verification and threat detection.
The challenge was to enable seamless and reliable data availability at the operational edge, while ensuring that the classified source environment remained fully isolated and protected from any potential cyber intrusion or backflow risk.
Solution deployed
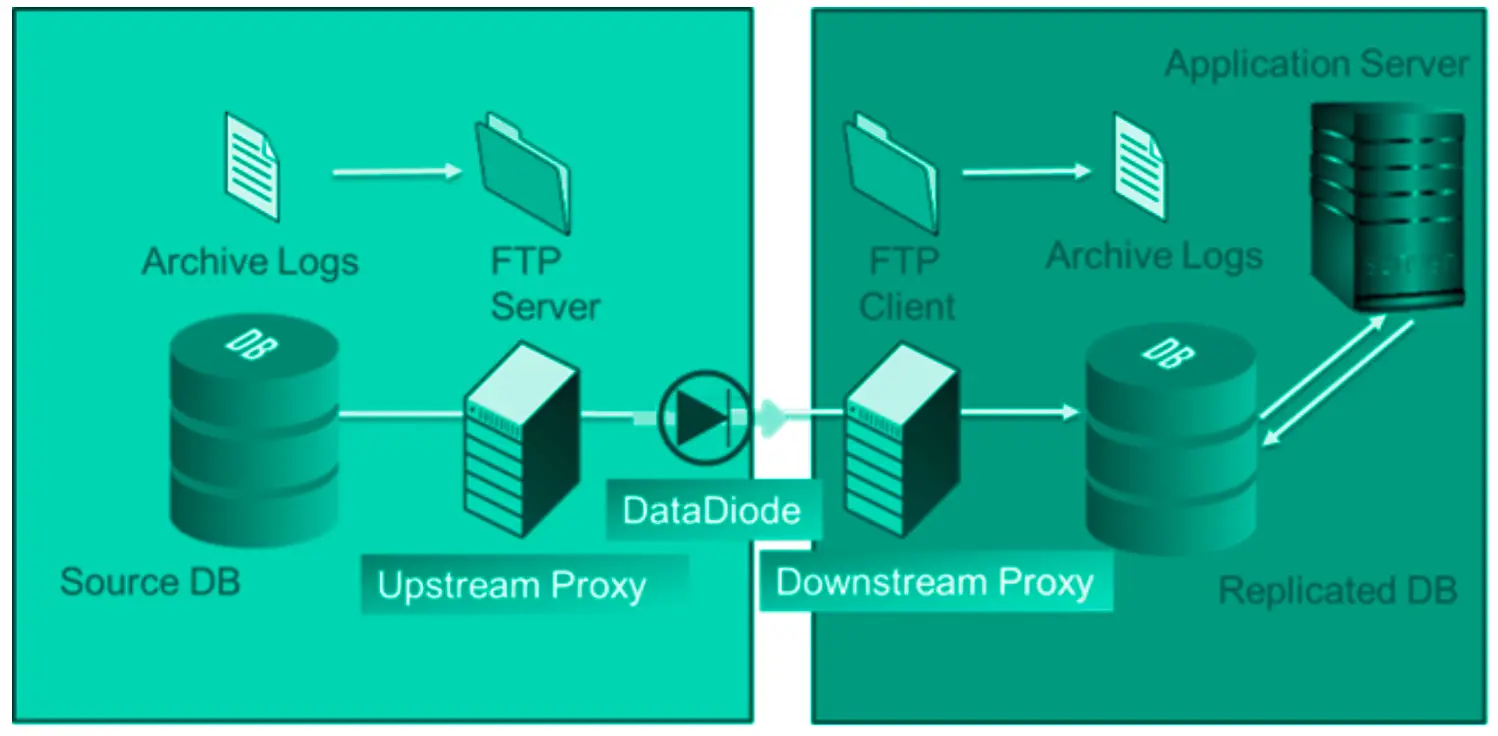
Cyberium implemented a resilient unidirectional replication architecture designed to ensure secure and continuous database distribution without exposing the source environment.
2x OWA 3U @ 1 Gbps
Hardware-enforced unidirectional gateway ensuring secure, one-way data transfer from the classified environment
MS SQL Differential Backup Agent
Enables efficient incremental database replication without direct database exposure
Standard Connector (SFTP)
Standard connector enabling structured and controlled file ingestion across domains
High-Availability℗ Setup
The architecture incorporates Cyberium patented High Availability mechanisms, ensuring uninterrupted data replication and eliminating any single point of failure for this critical operational data flow.
How It Works — Architecture Overview
Outcomes & benefits
The solution enabled secure operational use of sensitive data at scale while maintaining strict network isolation.
Real-time watchlist availability at checkpoints, enabling live identification of high-profile individuals
Zero cybersecurity incidents since 2018 despite serving over 100 million users annually
Continuous data availability with no compromise of the classified environment
More use cases
- Gov & Defense
- OWA 2U/3U
- Bitdefender, ClamAV
- SFTP, FTP/S/ES
- Gov & Defense
- OWA 2U/3U
- SFTP, FTP/S/ES
We secure the Sovereign
— connecting what should stay isolated.
Latest blog entries
- OT Cybersecurity Best Practices
Key takeaways A data diode concentrates trust — when it fails, nobody is looking for it One-way by component choice (…)
- Engineering Insights
Key takeaways – Cybersecurity Hardware OT networks need different hardware than IT networks — the threat model and operational constraints (…)
- OT Cybersecurity Best Practices
Key takeaways A data diode enforces one-way data transfer at the hardware level — not through software rules, but through (…)
- AI & Cybersecurity, Threat Landscape
Key takeaways In September 2025, GTG-1002 ran a full autonomous intrusion campaign across 30 organizations — AI handled 80 to (…)
- AI & Cybersecurity
When a firewall sits at the boundary between your IT network and your OT environment, you’re trusting a policy. A (…)
- AI & Cybersecurity, Threat Landscape
The rules of industrial cybersecurity changed in 2026. For years, the standard playbook held: segment your network, deploy a firewall (…)